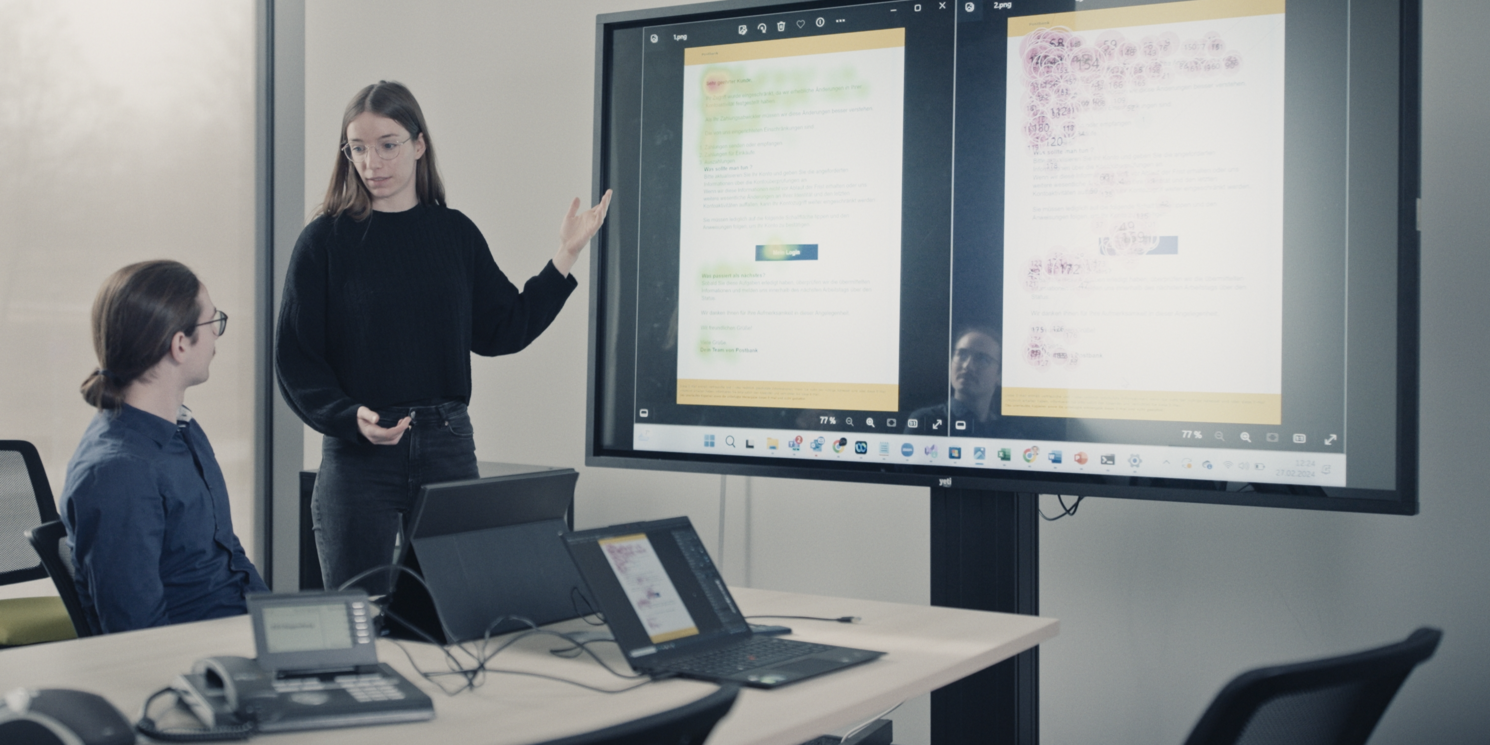
The logo was right and the threat was unmistakable: anyone who failed to click on the link would have their customer account deactivated. Only the sender’s address was missing a single letter – an “e”. Of the ten participants in an eye-tracking study at OTH Regensburg who were wrong most often, eight believed the email was genuine. This scam is known as phishing: criminals disguise emails as messages from a well-known company in order to get hold of passwords, data or money.
Meret Kristen and Fabian Engl, research associates at the Software Engineering Laboratory for Safe and Secure Systems (LaS³) in the Faculty of Electrical Engineering and Information Technology at OTH Regensburg, are investigating where people look before deciding whether an email is genuine or fake. “A system is only as secure as the person using it,” says Kristen. According to the 2025 Data Breach Investigations Report by the US company Verizon, the human element played a role in around 60 per cent of the data breaches analysed – through deception, errors or unintentional actions.
Wrong decisions despite IT security training
Sixty per cent of the participants had previously attended anti-phishing training – and yet they were no better at spotting fakes than the rest. “To be honest, that surprised me,” says Kristen. “But we all know it from data protection or health and safety training: you let it wash over you, and online you click through as quickly as possible.” Even those with a good knowledge of IT security made their decisions faster, but were not right any more often. For Kristen, the problem lies elsewhere: “People don’t click on a phishing email because they couldn’t see through it, but because they’re distracted and want to get through their inbox quickly.”
“Normally, all you get at the end of a phishing study is the result: right or wrong,” says Prof. Dr Jürgen Mottok, who teaches computer science at OTH Regensburg with a focus on IT security and functional safety, and heads LaS³. “With eye-tracking, we can see how a decision comes about – what someone pays attention to and what they overlook. That allows us to develop training that genuinely helps in everyday working life.”
The most dangerous bait: attachments
For the study, the team – working within the EU project “Digitale Innovation Ostbayern” (DInO, Digital Innovation Eastern Bavaria) – took nine mobile eye-trackers to small and medium-sized enterprises and public authorities in the region. On site, 103 employees viewed 18 emails in a familiar Outlook interface, twelve of which were real phishing attempts. The eye-trackers are slim bars attached to the screen. Two cameras inside them capture the pupils and the reflections of light on the cornea, and use these to calculate where someone is looking 250 times per second. DInO came to an end in late August; in the follow-up project dina (Digital Innovation and AI), the team continues to offer companies and public authorities eye-tracking studies and advice on IT security.
On average, participants identified just over ten of the twelve fakes. Emails with attachments were the most dangerous: almost one in five slipped through, compared with around one in seven for emails containing a link and around one in nine for payment requests. Conversely, participants took one in five genuine emails for a scam. The findings were presented at the SECURWARE 2024 conference and published in the International Journal on Advances in Security.
Brief, darting glances lead to wrong decisions
A pattern emerges from the gaze data: those who were often wrong tended to cast only brief glances at the sender, the attachment and the text, jumping back and forth between them. Those who spotted every fake took more time over the crucial details. Looking alone is no protection, however: faced with an email from an unfamiliar shoe shop, one participant focused mainly on the suspicious ZIP attachment – and still believed the email was genuine. Several participants pointed out themselves that ZIP files are still common in smaller businesses today.
Engl puts the success of a fake email about a supposedly blocked account down to habit: “If a company hardly anyone has heard of writes to me, I’m sceptical at first. But if that’s where I have my Deutschlandticket [Germany’s nationwide public transport pass] or my internet contract, I’m used to emails like that – and I trust the brand.”
When a typo inspires trust
The scam emails themselves have improved over the years. “It’s no longer that dubious prince who wants your money,” says Engl. For a long time, spelling mistakes were regarded as a reliable warning sign. Now that AI programs can write flawless text, they are of little use for that any more. Engl even considers it conceivable that, in future, a typo might be more likely to inspire trust. He points to a US study involving more than 3,000 participants: a chat-based customer service agent that made a typo and corrected it came across as more human and warmer, and in some cases more helpful too. “So really, we’re back to square one,” says Engl.
The team is now investigating how far people trust AI. An initial finding from a study that has not yet been published: if the AI also rates its own text with a graphical score from 1 to 5, people read less of the text itself when the score is high. “All you see is: OK, that’s good,” says Engl. “Then I don’t need to read it through in detail.”
The PHP security vulnerability “PHP2Shell”, which put websites around the world at risk, shows how quickly AI is changing IT security: it was found with the help of AI, and millions of attempted attacks have since been recorded. Questions like these will also be the focus of the IT Security Day “KI: Risikofaktor oder Werkzeug?” (“AI: Risk Factor or Tool?”), to which OTH Regensburg and the University of Regensburg are inviting their students and staff on 11 November 2026.
Partnership with a Scottish university
Since this summer, cybersecurity research at OTH Regensburg has been strengthened by a partnership with Abertay University in Dundee, Scotland. Plans include joint research and publications, guest lectures and joint student projects. In Dundee, Dr Lynsay Shepherd uses eye-tracking to study how people make security decisions and when they trust technology and AI systems. These are the same questions that are on the table in Regensburg: what do people pay attention to before they believe an email – or a machine?